
What it does today
- Passwordless sign-in with one-time codes by email, or by SMS for Indian numbers; you choose which methods are open and which comes first
- Single sign-on across all your connected apps with one account
- Open standards: OAuth 2.0 and OpenID Connect (Authorization Code with PKCE), signed ID tokens with published keys, refresh tokens, userinfo
- Consent: people see and approve what each app may read (profile, email, phone)
- Verified contact details shared with your apps
- Organisations for business and community apps
- Account self-service: profile, contact details and sign-in settings
Signing in to your app
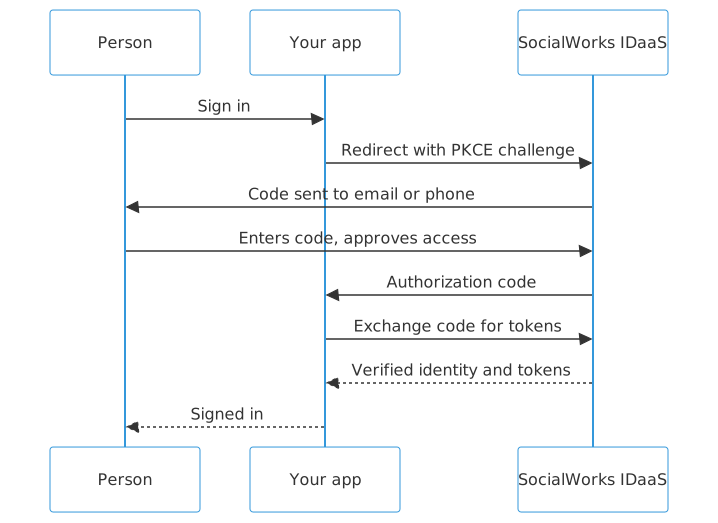
Text version of this diagram
- Person → Your app: Sign in
- Your app → SocialWorks IDaaS: Redirect with PKCE challenge
- SocialWorks IDaaS → Person: Code sent to email or phone
- Person → SocialWorks IDaaS: Enters code, approves access
- SocialWorks IDaaS → Your app: Authorization code
- Your app → SocialWorks IDaaS: Exchange code for tokens
- SocialWorks IDaaS → Your app: Verified identity and tokens
- Your app → Person: Signed in
What ServerWorks does for you: registers your apps, configures sign-in methods, scopes and redirect addresses; builds the integration into your web or mobile apps; migrates existing users; runs, monitors and supports the service.
Not yet available: SAML 2.0 and sign-in through your own directory (Active Directory, Entra ID); user provisioning (SCIM); authenticator-app or passkey MFA; an uptime SLA.
CTA: Request early access.
Questions
Does it work with our framework?
Any framework that supports OpenID Connect can connect.
Where is the data hosted?
Region.